Critical Firewall Vulnerability: What to Do in the First 48 Hours
2026
Critical firewall vulnerabilities are among the most urgent network security risks IT teams can face. Firewall vendors regularly publish critical security advisories, sometimes for vulnerabilities that are already being actively exploited.
When that happens, the question is not only whether a patch is available. Organizations first need to understand their exposure, reduce the immediate risk, safely patch their firewall infrastructure and verify that no compromise has already taken place.
A structured firewall vulnerability management process can make the difference between a controlled response and a security incident that escalates.
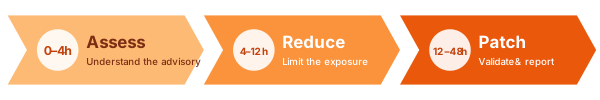
0–4h — Assess
Understand the advisory
4–12h — Reduce
Limit the exposure
12–48h — Patch
Validate & report
Hours 0–4: Assess the Firewall Vulnerability Before You Act
The first reflex when a critical firewall vulnerability is announced is often to patch immediately. However, an effective vulnerability response starts by understanding the advisory and determining the actual risk to your environment.
- which firewall versions and features are affected;
- whether the vulnerable component is reachable from the internet;
- whether the affected functionality is actually enabled;
- whether the vulnerability is already being actively exploited.
A vulnerability in an unused feature carries a very different risk than one affecting a publicly accessible VPN portal.
This initial assessment is an essential part of effective firewall security and vulnerability management: it allows IT teams to prioritize action based on actual exposure rather than severity scores alone.
Hours 4–12: Reduce the Exposure
Installing a hotfix on a production firewall often requires a maintenance window and a rollback plan. Until the patch can safely be installed, temporary security measures can significantly reduce the risk.
- restricting access to management interfaces and portals to known IP addresses;
- disabling affected features that are not in use;
- activating IPS protections released by the vendor;
- checking firewall and security logs for signs of prior compromise.
When a firewall vulnerability is already being actively exploited, patching alone is not enough. You also need to determine whether an attacker may have reached the environment before the vulnerability was remediated.
This makes log monitoring and compromise checks an important part of the wider network security incident response process.
Hours 12–48: Patch, Validate and Report
Once the immediate exposure has been reduced, the affected firewall infrastructure can be updated.
In clustered environments, updates can be applied member by member using controlled failover to minimize the impact on users and business operations.
After patching, validate all critical services, including:
- VPN tunnels;
- cluster status;
- firewall policy installation;
- logging and monitoring;
- other services affected by the maintenance.
The final step is documentation.
A clear report should record:
- the identified firewall vulnerability;
- the systems that were affected;
- the level of exposure;
- the actions taken;
- the outcome of the validation;
- any remaining follow-up actions.
A documented process makes future vulnerability response more consistent and provides evidence of the measures taken.
Firewall Vulnerability Management, NIS2 and CyberFundamentals
Effective firewall vulnerability management is not simply about installing security patches.
Organizations need a repeatable process to:
- identify vulnerabilities;
- assess their exposure and impact;
- prioritize remediation;
- reduce immediate security risks;
- patch affected systems;
- validate that security controls still function correctly;
- document the actions taken.
The Belgian NIS2 law relies on the CyberFundamentals (CyFun®) framework of the Centre for Cybersecurity Belgium (CCB), and the process described above supports several of its requirements.
- RA-08.1 — establishing a vulnerability management plan to identify, analyse, mitigate and communicate vulnerabilities;
- RA-02.1 — receiving threat and vulnerability information such as vendor security advisories;
- AE-03.1 — enabling, retaining and reviewing logs to detect unusual activity;
- AM-08.2 — installing patches and security updates on critical system components;
- AM-08.10 — verifying that security controls still work after maintenance or patching.
A documented and repeatable vulnerability management process therefore supports both IT security and compliance requirements.
Our Practical NIS2 Guide for IT infrastructure professionals provides a broader overview of the key actions and priorities to translate NIS2 requirements into a more resilient IT infrastructure. Download our NIS2 Guide.
How to Prepare Before the Next Critical Firewall Vulnerability
Critical vulnerabilities cannot always be avoided, but their impact can be controlled.
Organizations that respond effectively typically have:
- an up-to-date inventory of firewall versions and exposed services;
- management interfaces that are never directly exposed to the internet;
- defined vulnerability management procedures;
- monitoring and logging in place;
- clear agreements about who can approve emergency maintenance and how quickly.
With a managed firewall and network security service, these processes can already be established before the next critical advisory appears.
That means your IT team does not have to start from zero when every hour counts.
Frequently Asked Questions About Firewall Vulnerabilities
A firewall vulnerability is a security weakness in firewall software, firmware or functionality that could potentially be exploited by an attacker. The actual risk depends on factors such as the affected feature, the firewall configuration and whether the vulnerable service is exposed to the internet.
Start by determining whether your firewall versions and configurations are affected. Assess the exposure, apply temporary mitigation measures where necessary, review logs for possible compromise and plan the security update using a controlled maintenance and rollback procedure.
The urgency depends on the severity of the vulnerability, whether it is actively being exploited and how exposed the affected system is. Vulnerabilities affecting internet-facing services and vulnerabilities known to be exploited require particularly rapid action.
Firewall vulnerability management is the structured process of identifying, assessing, prioritizing, mitigating, patching and monitoring vulnerabilities affecting firewall infrastructure.
A structured vulnerability management process supports several CyberFundamentals requirements referenced in the Belgian NIS2 context, including vulnerability identification, security monitoring, patch management and validation after maintenance. Read more about NIS2 in our practical guide.
October 2026
Nicolas Dricot